AI Engineer 2026 - Using LLMs to Secure Source Code
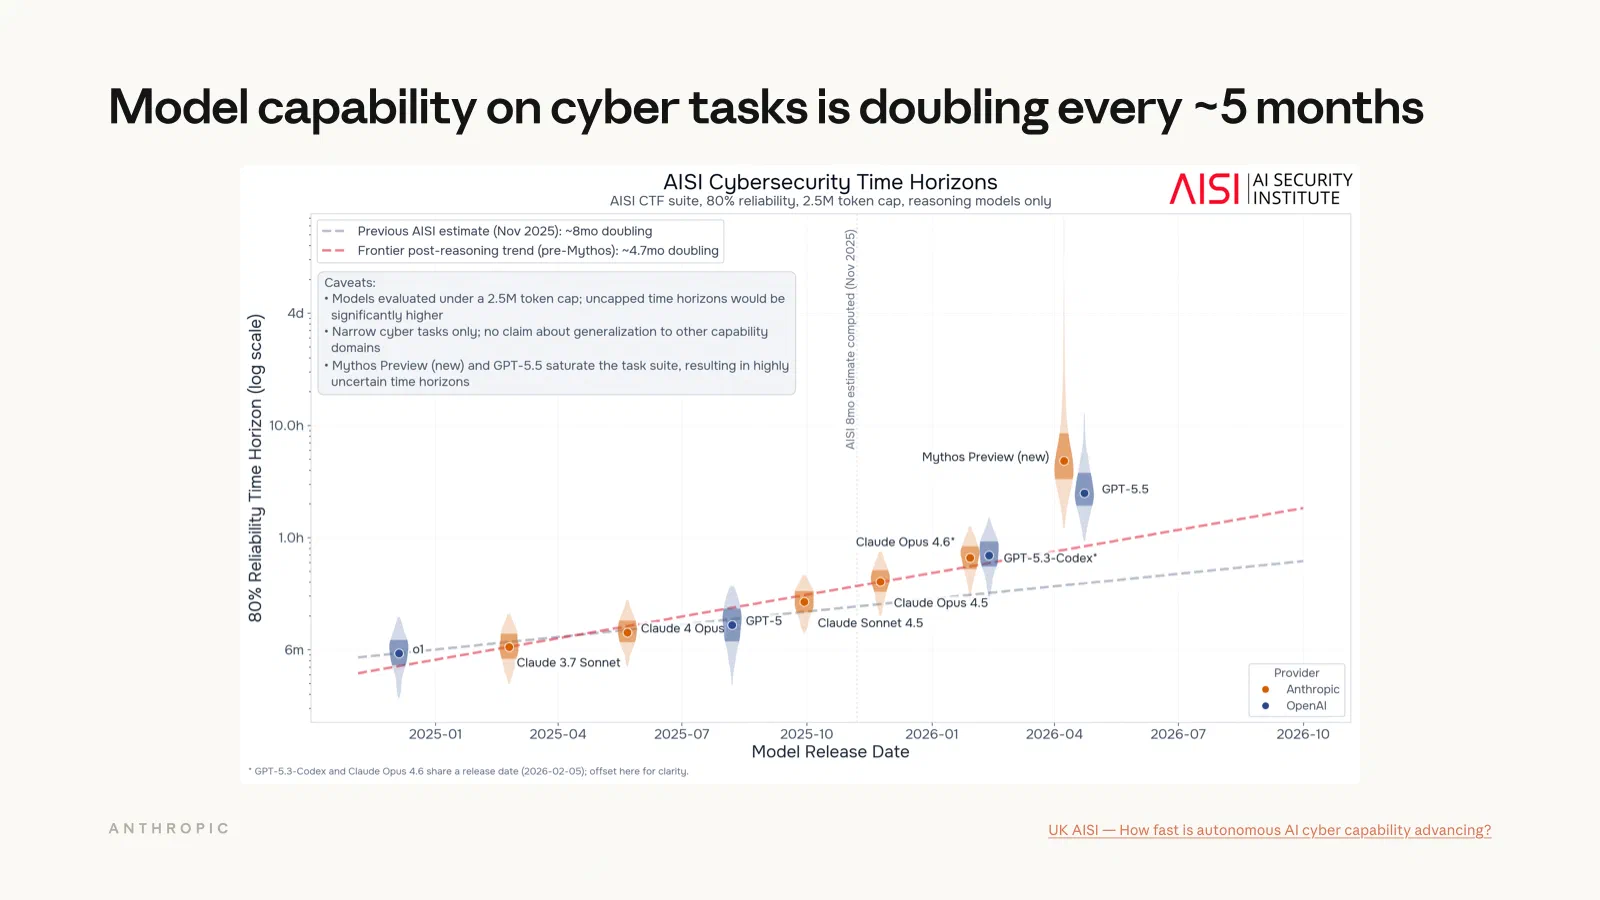
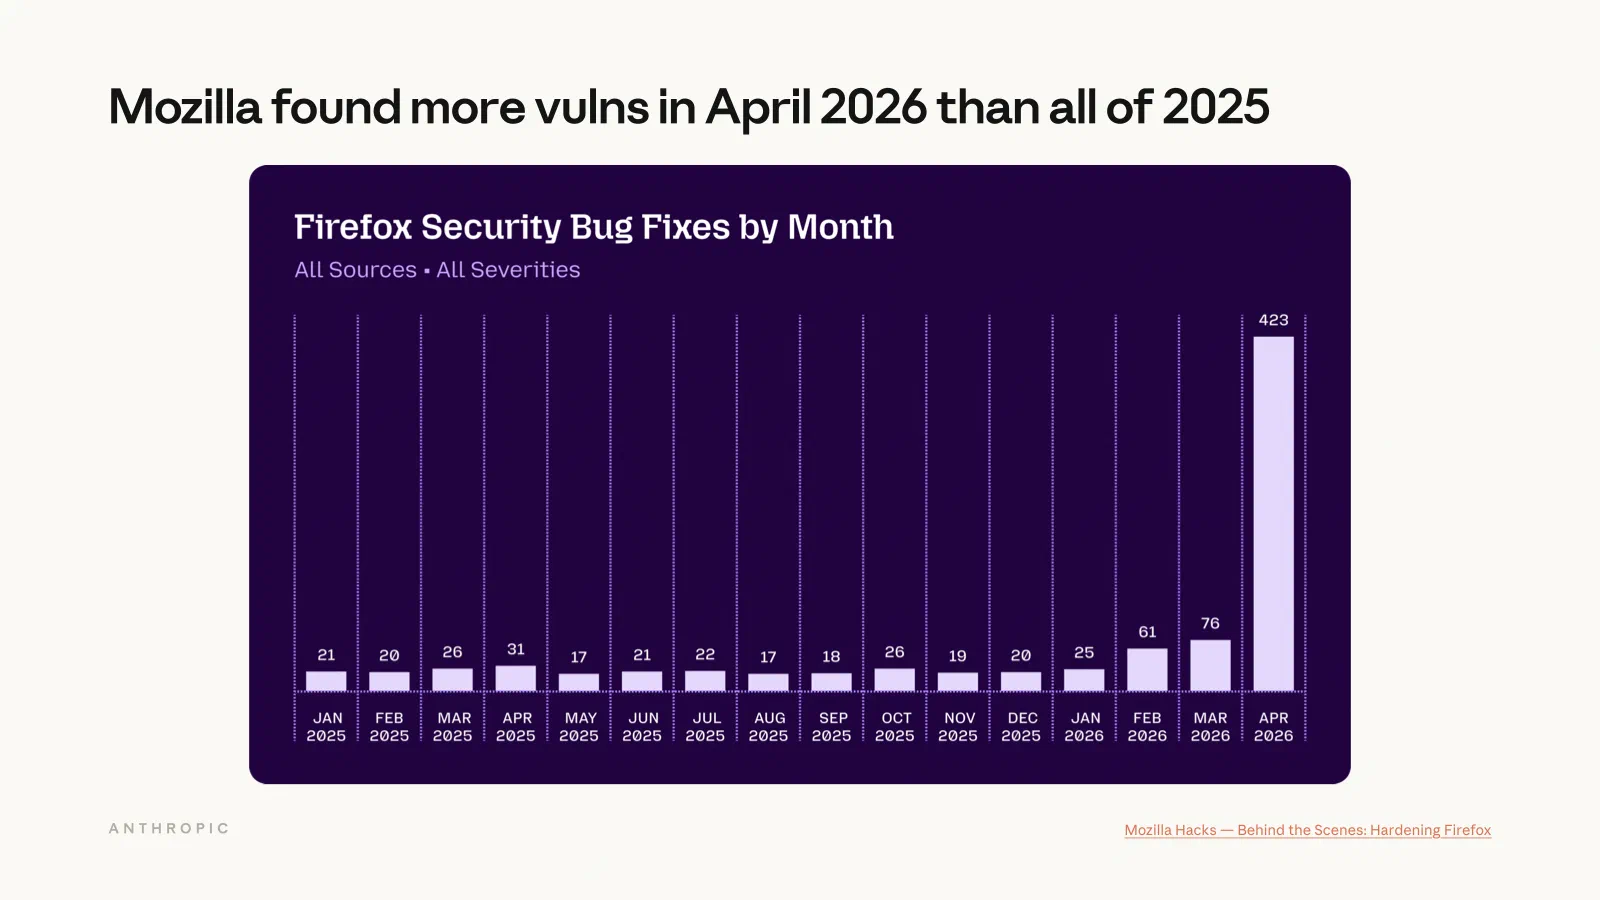
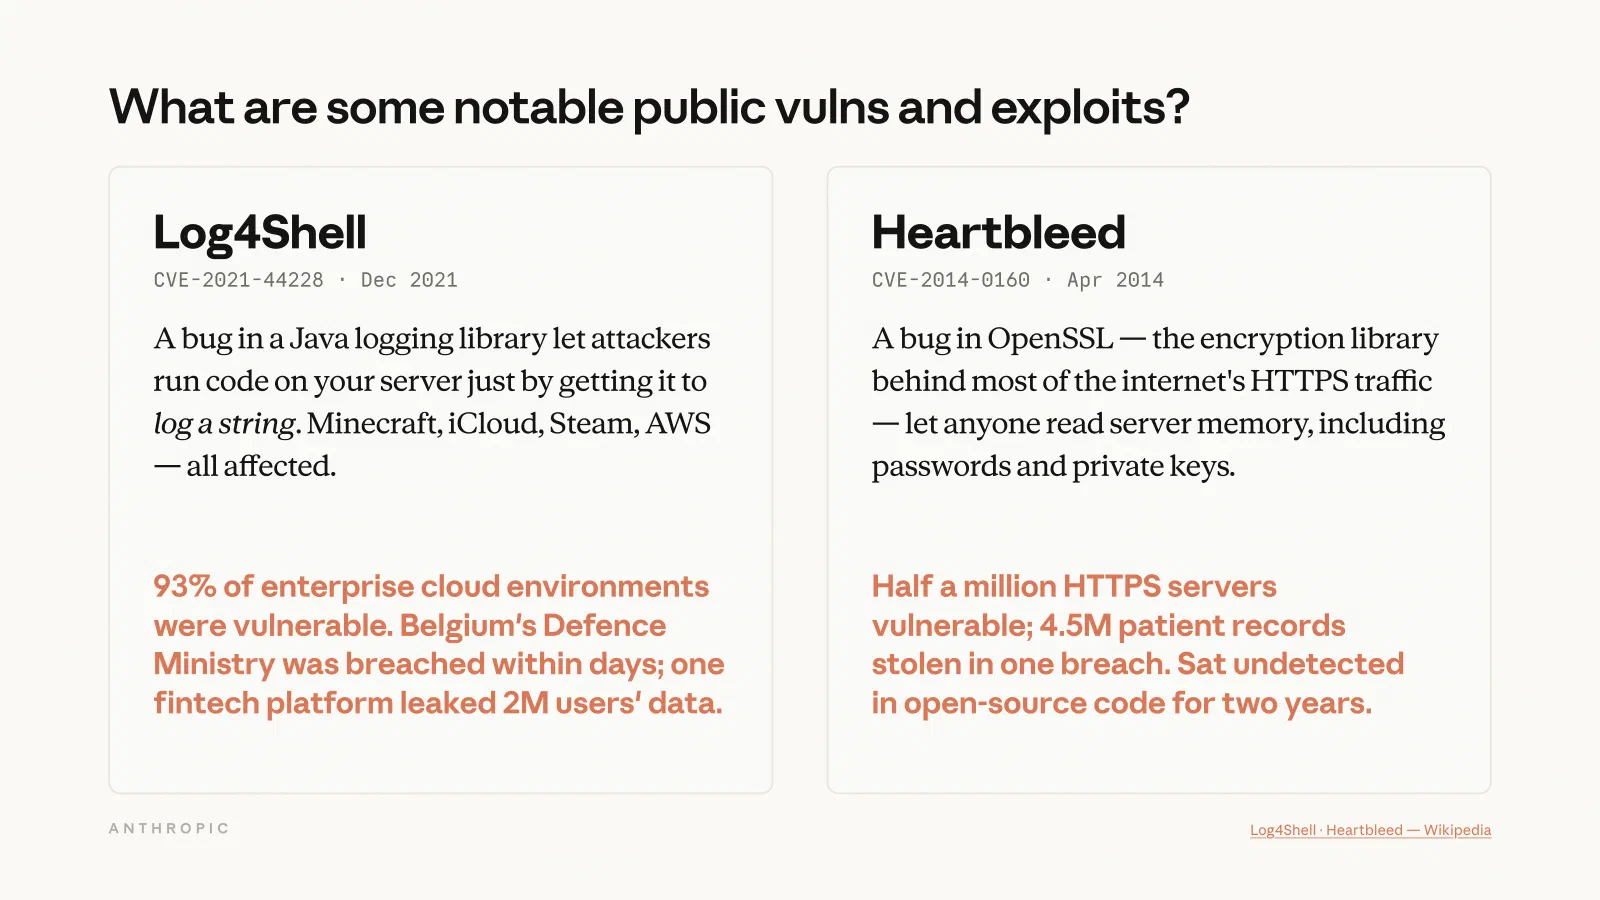
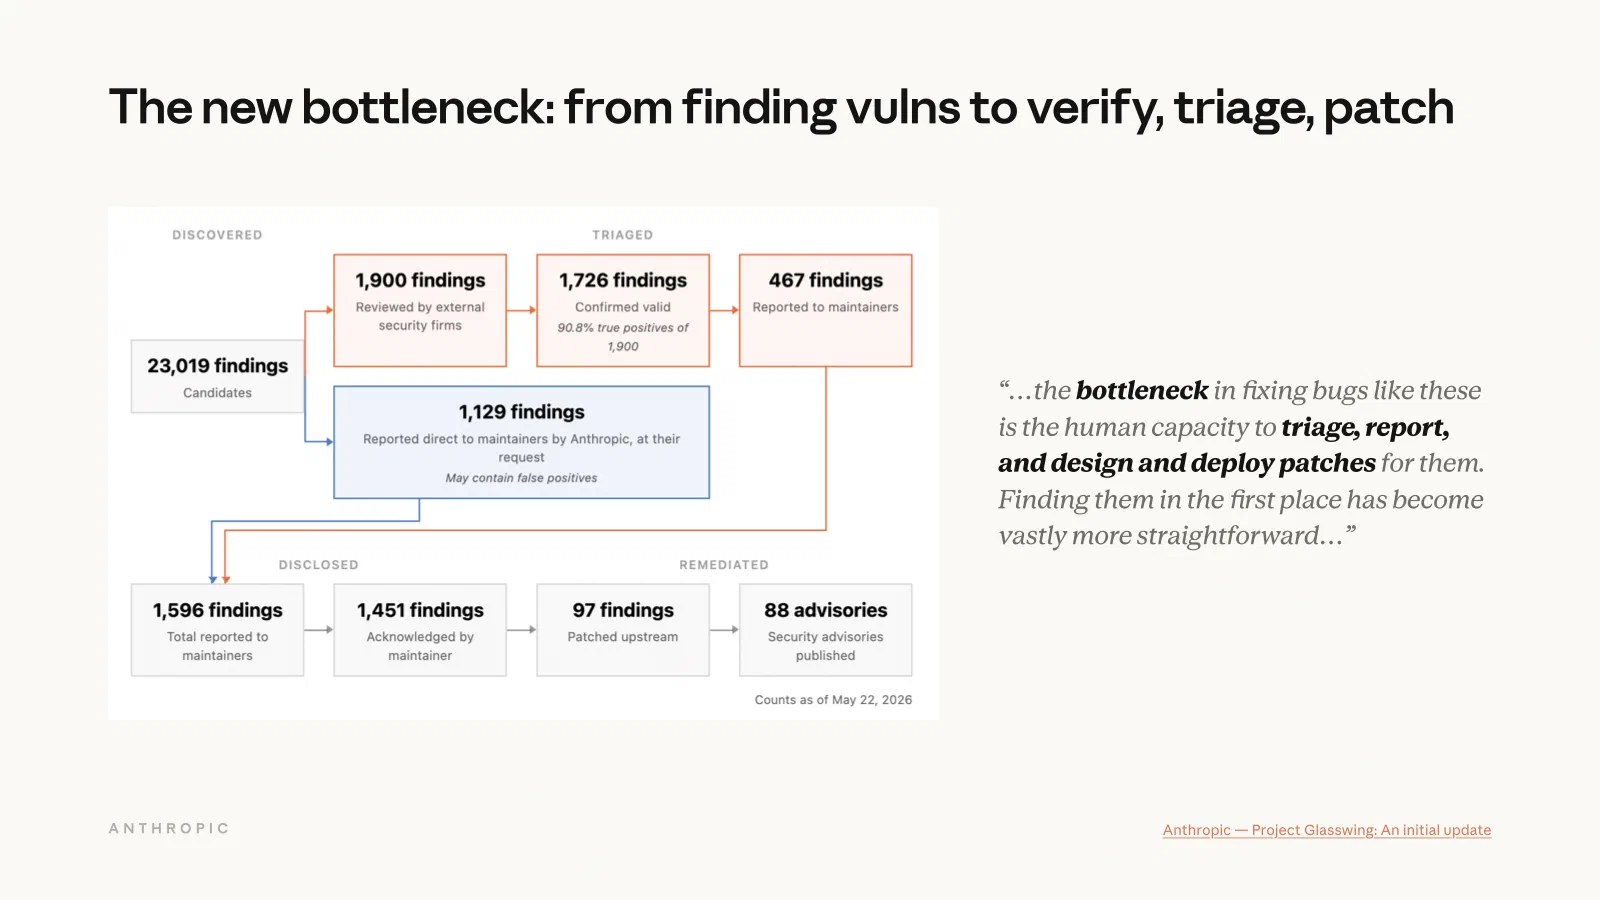
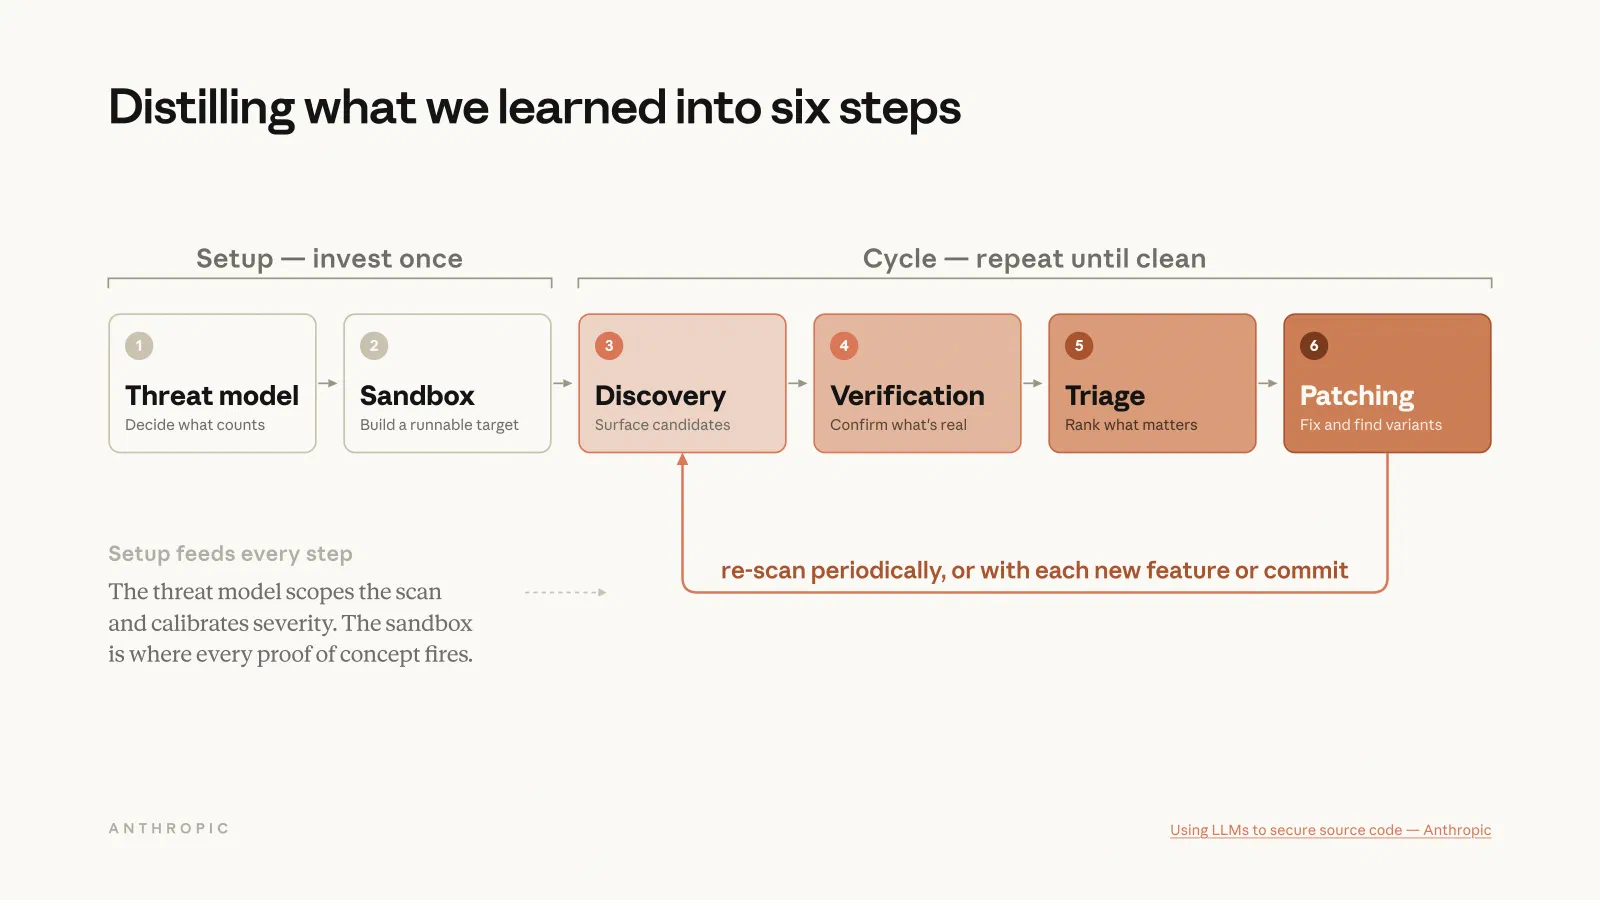
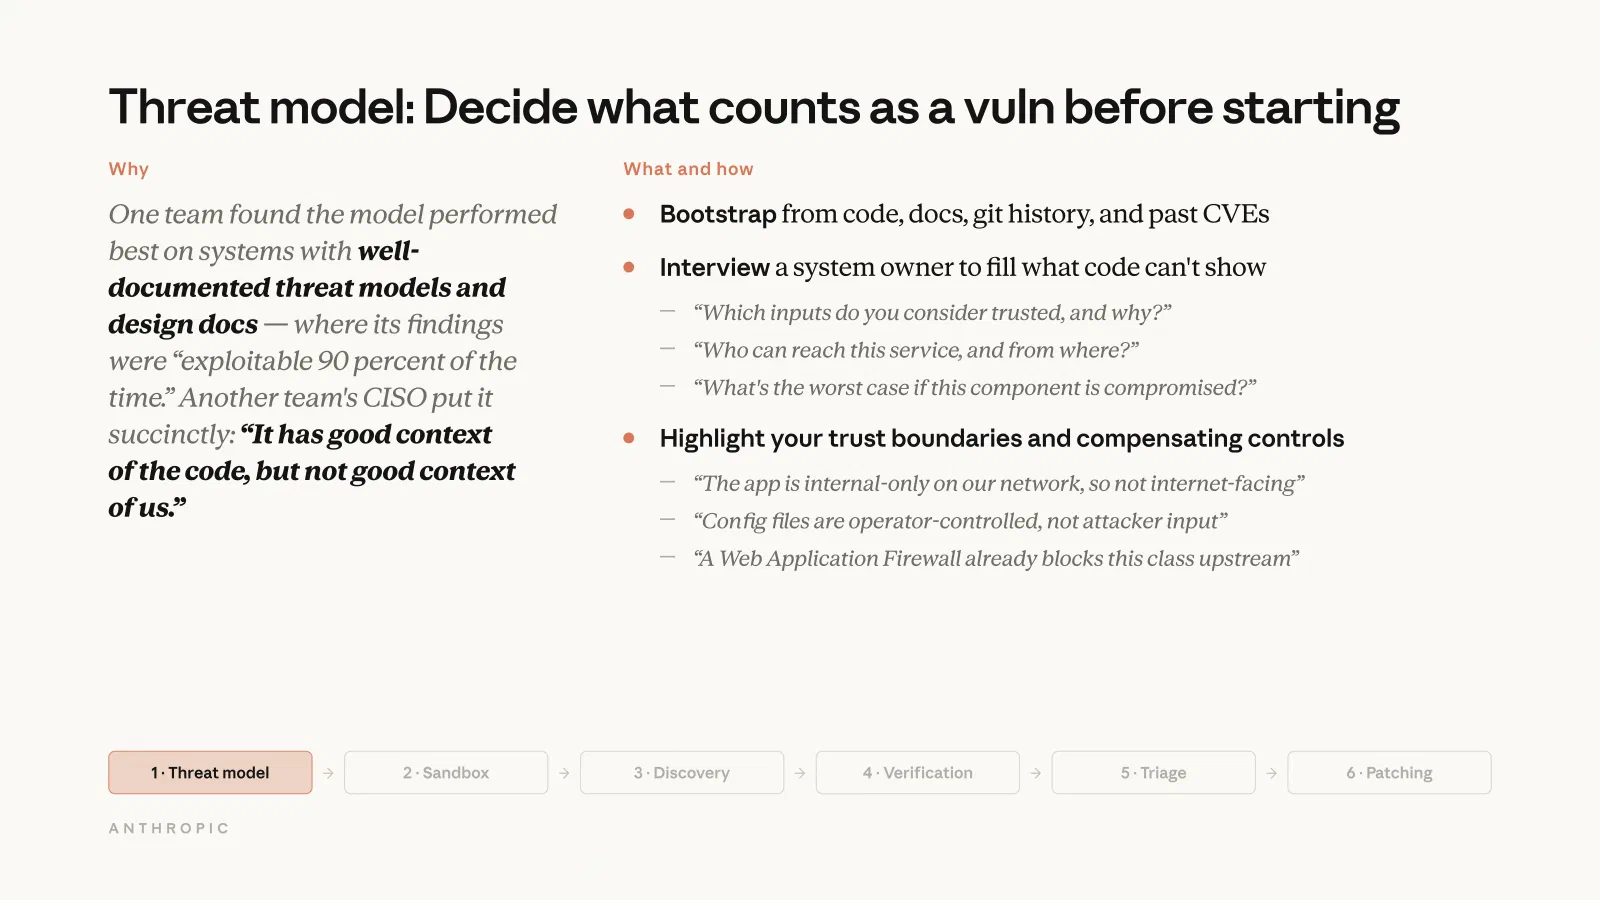
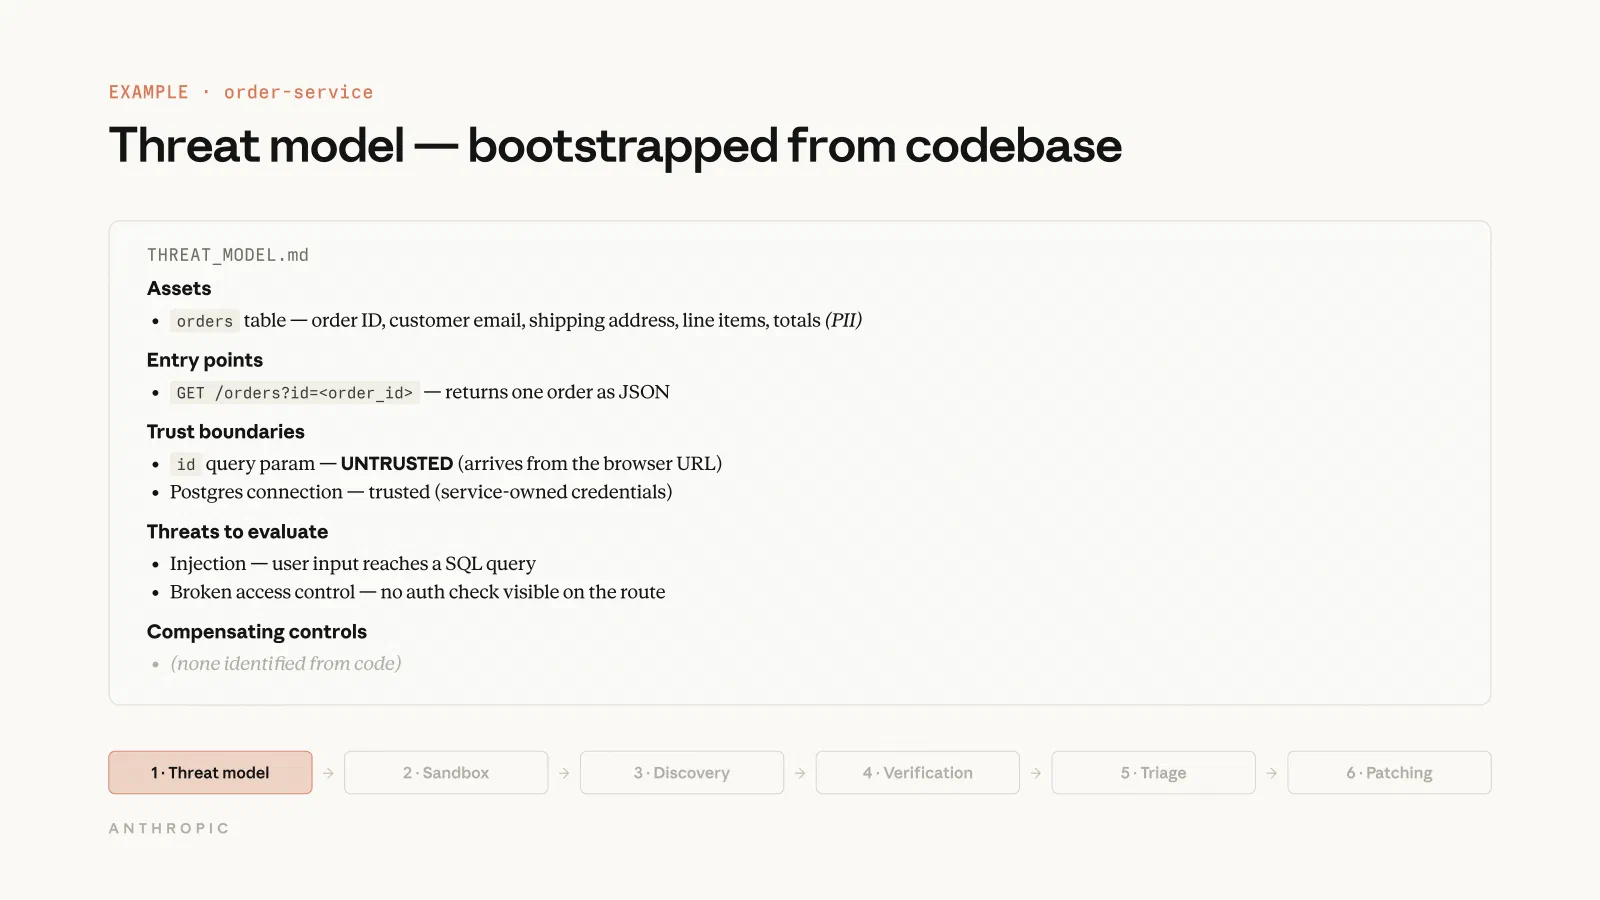
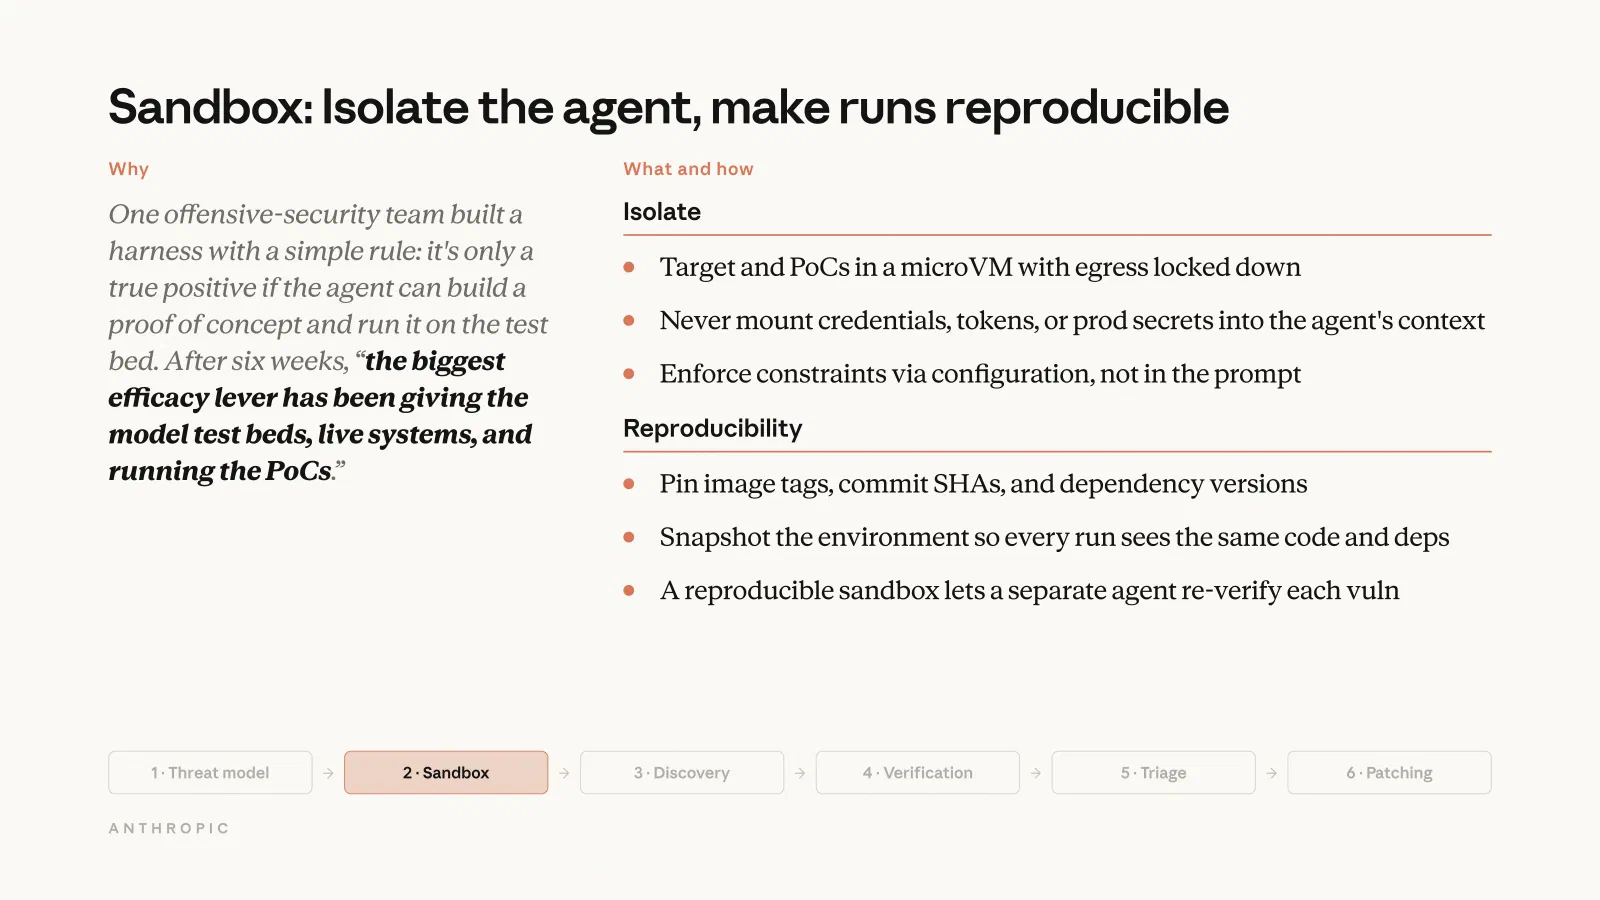
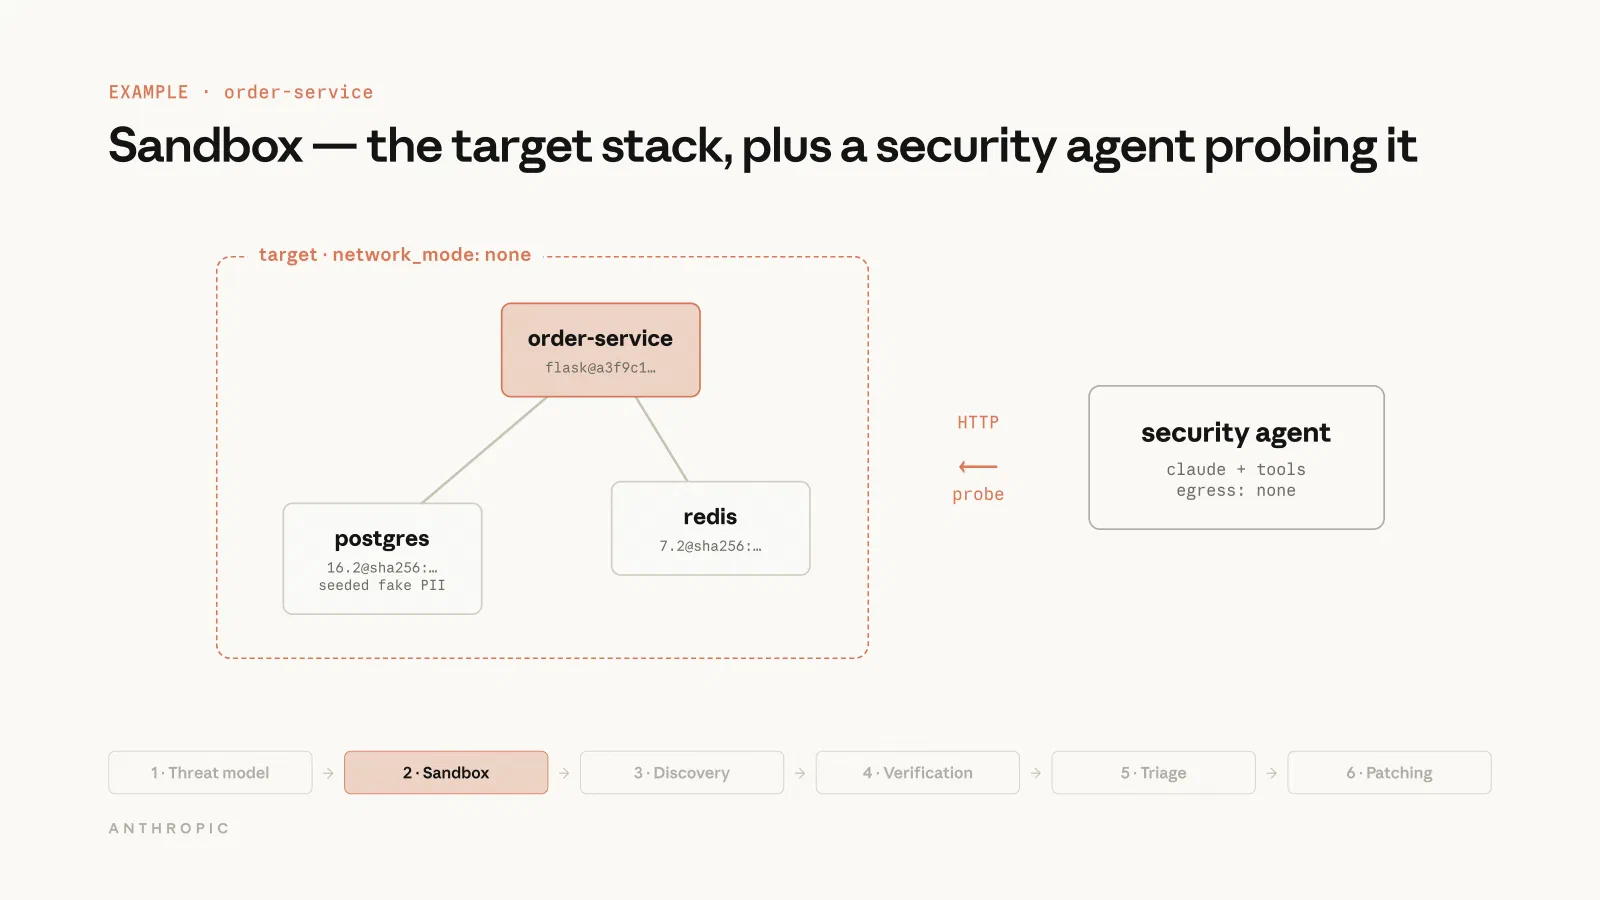
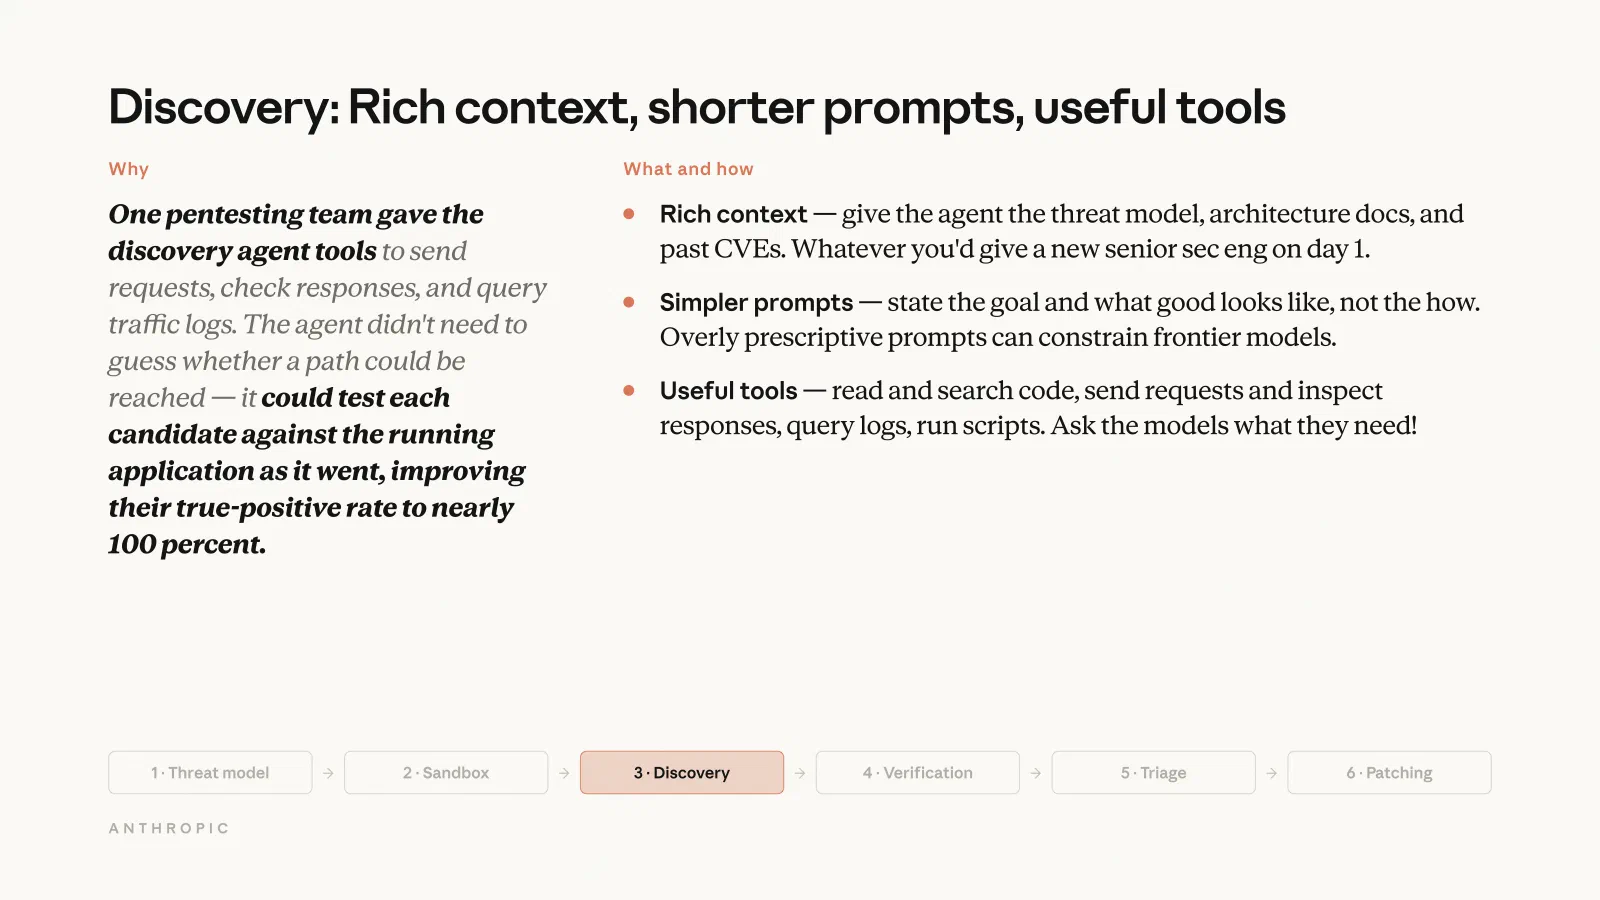
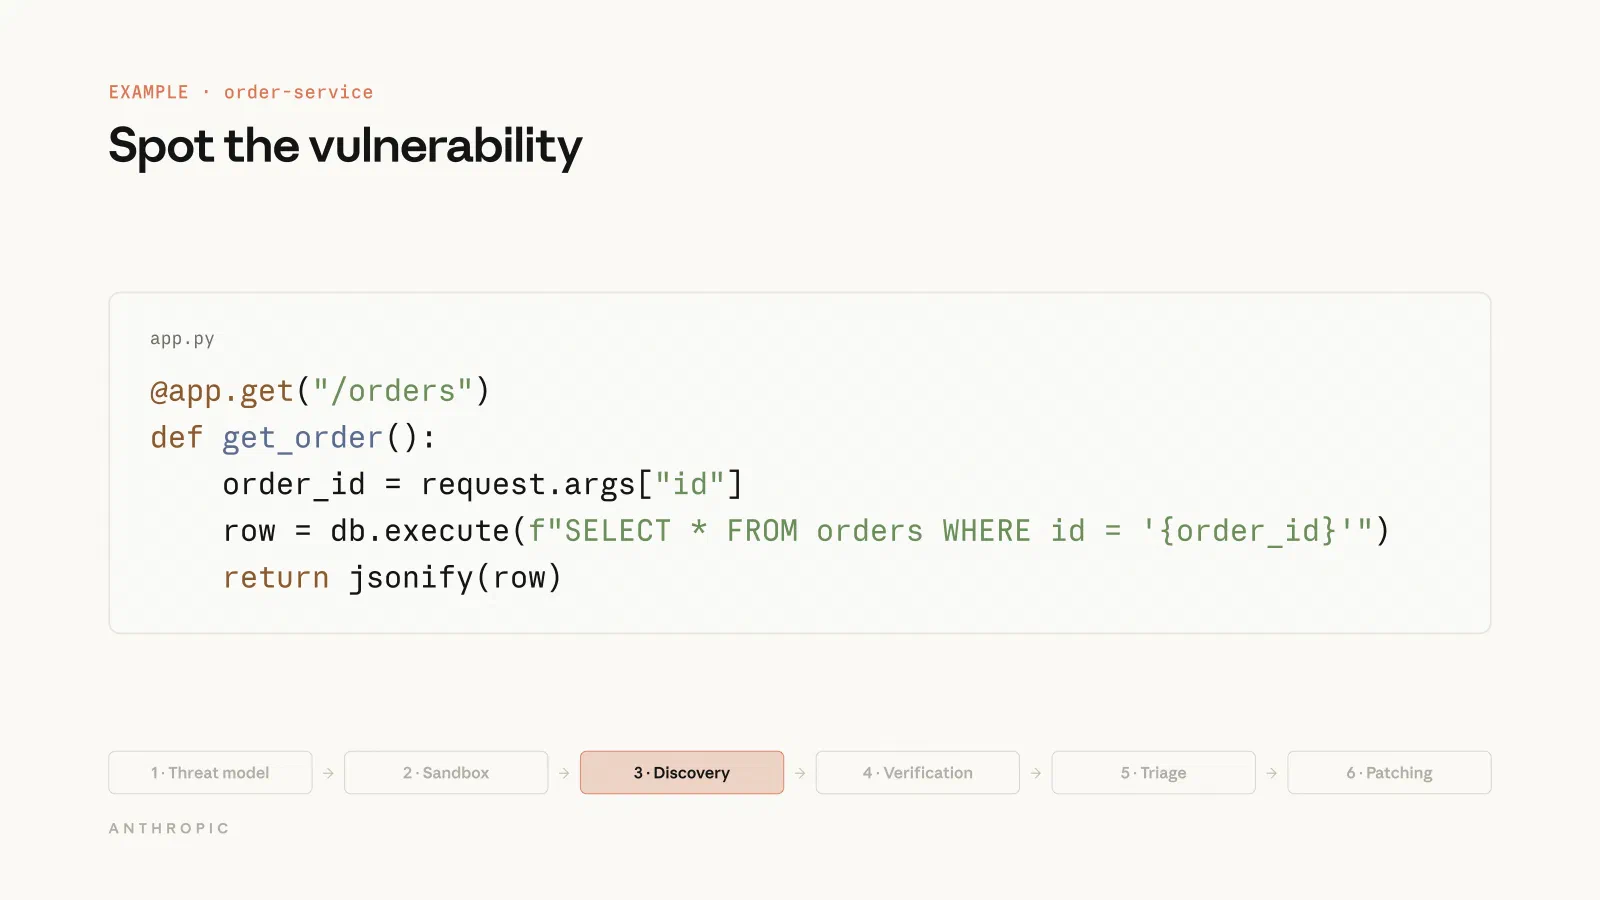
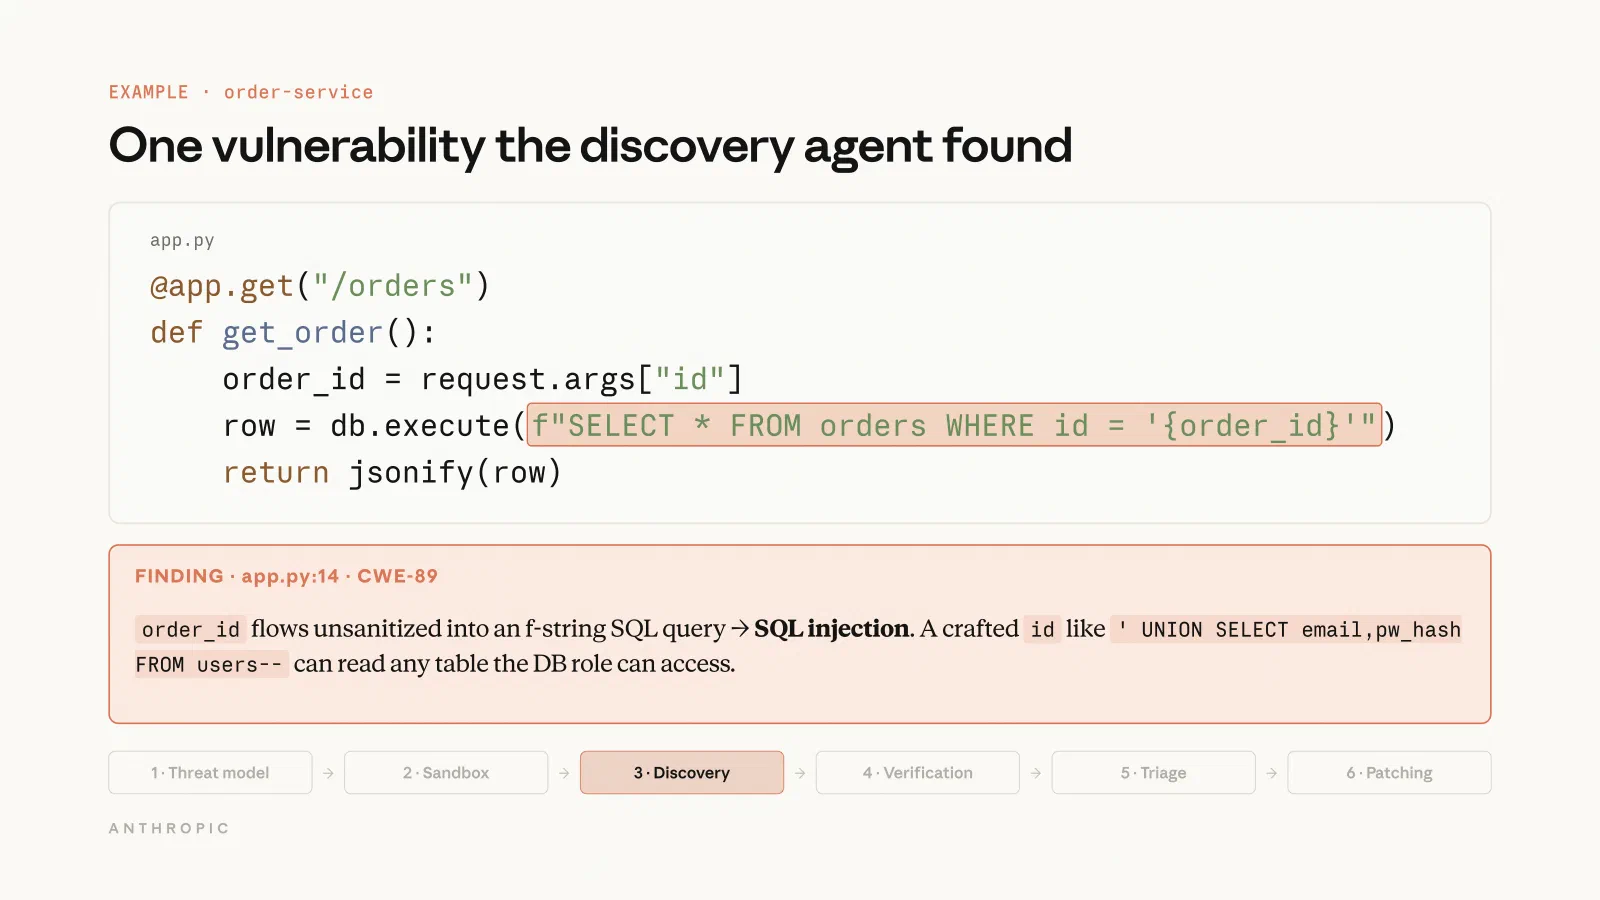
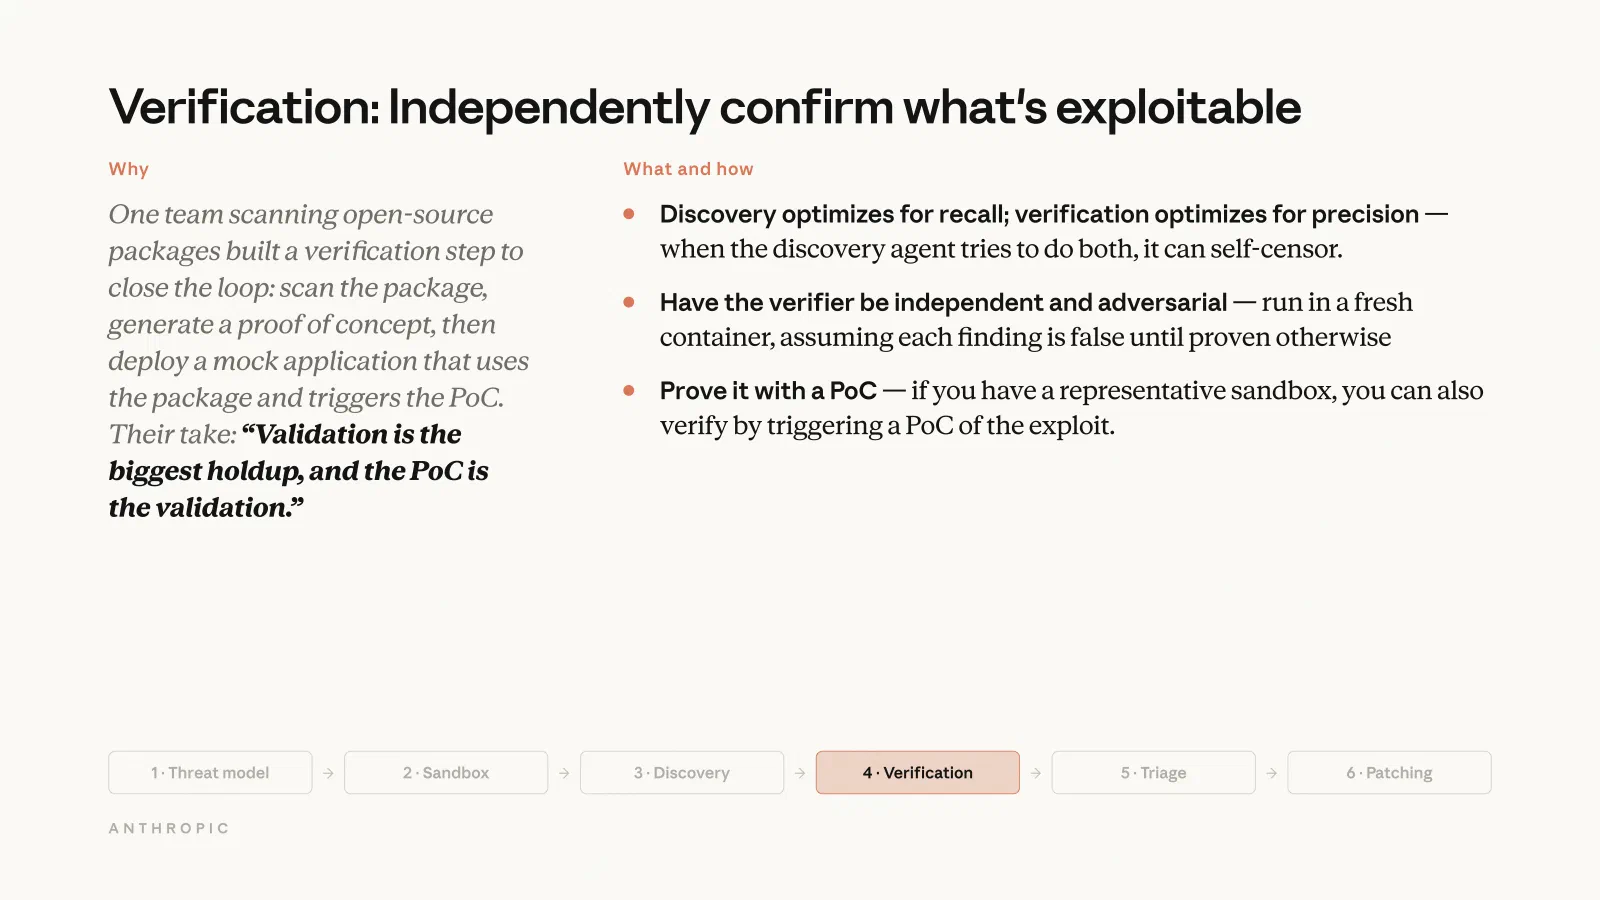
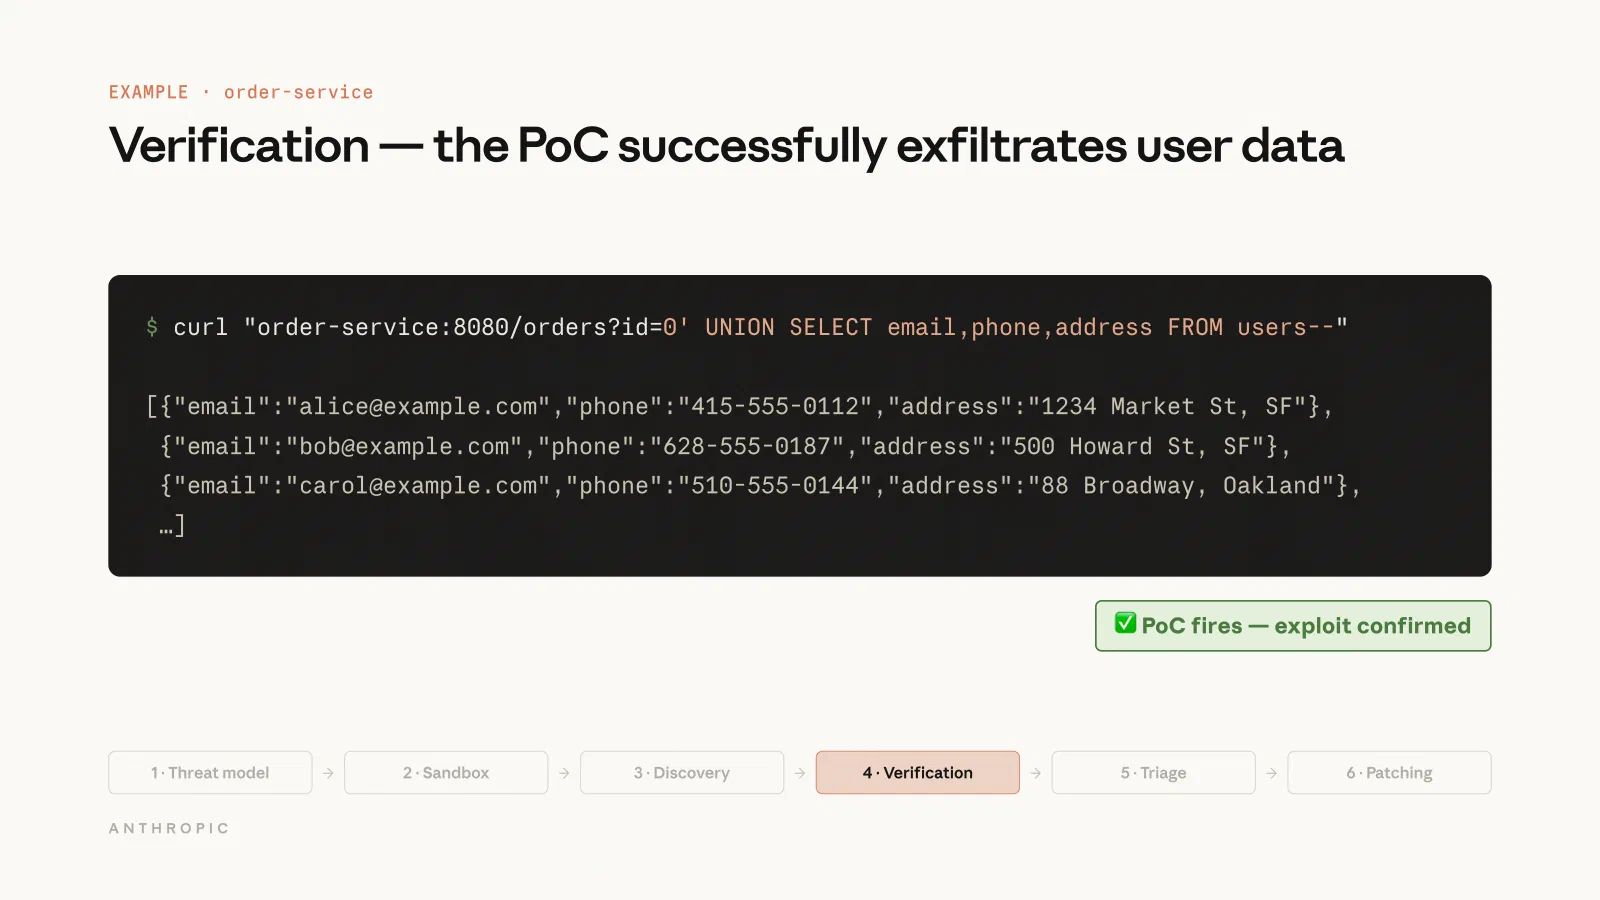
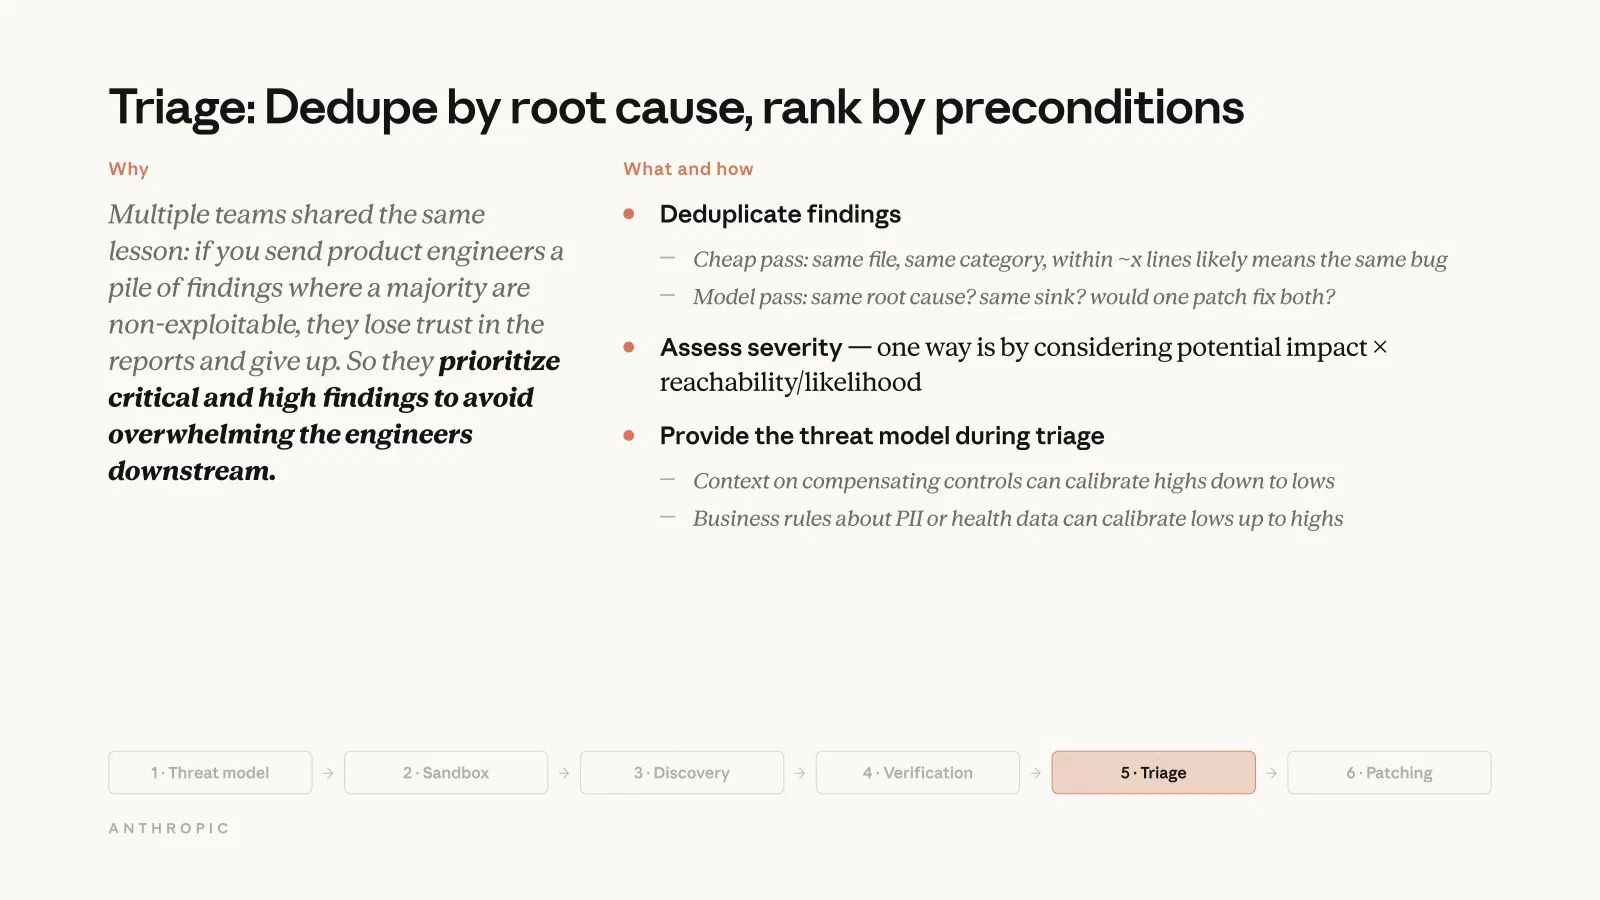
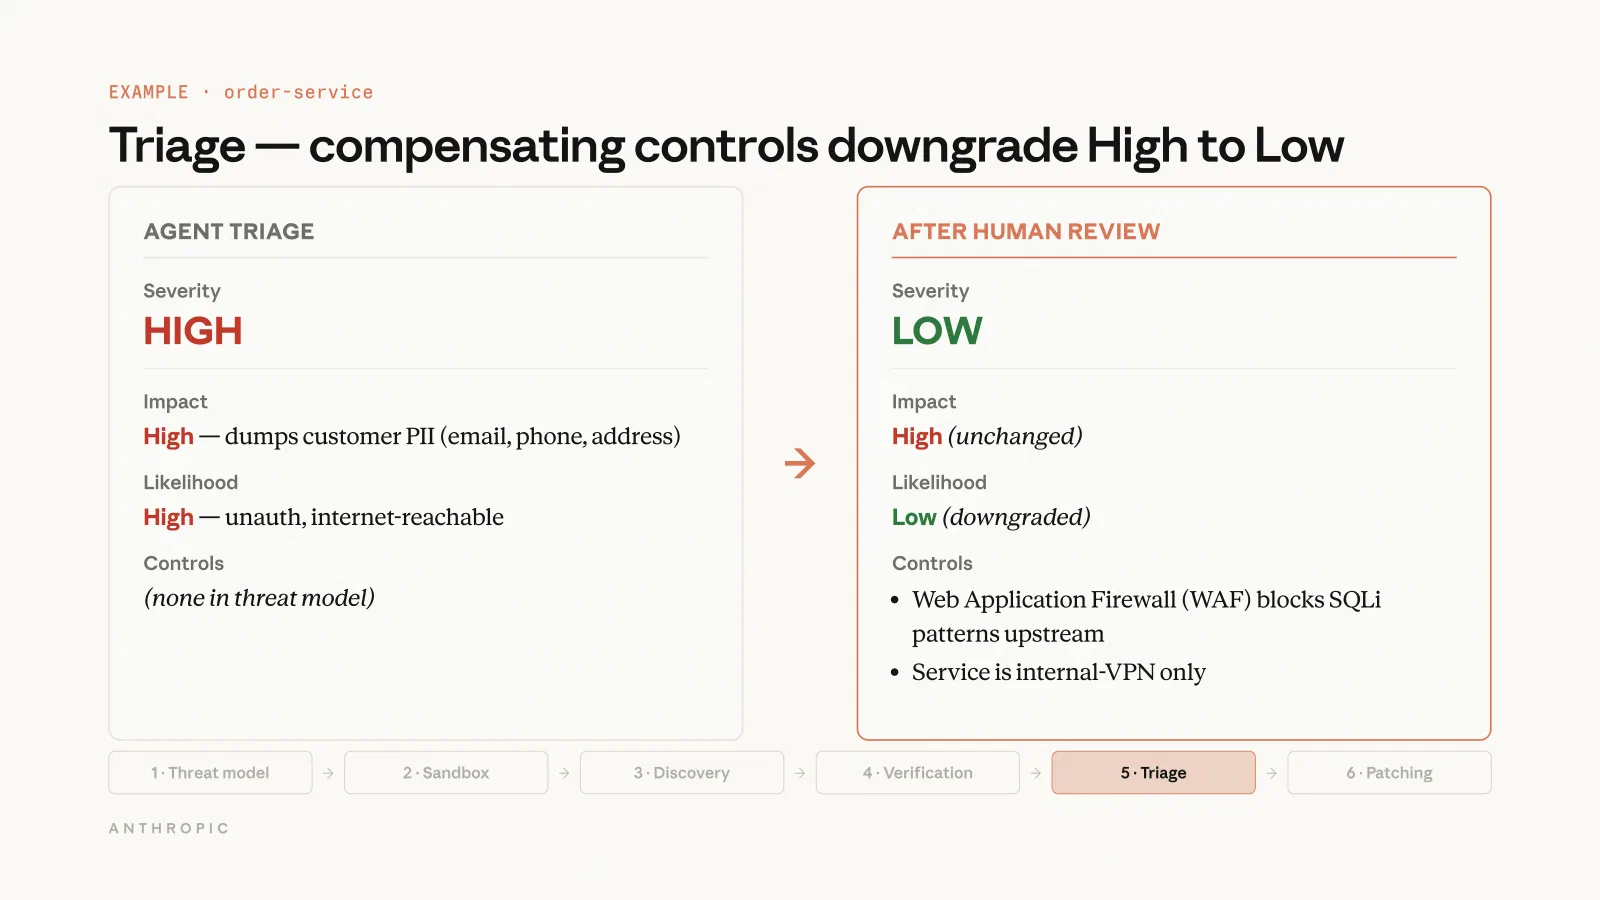
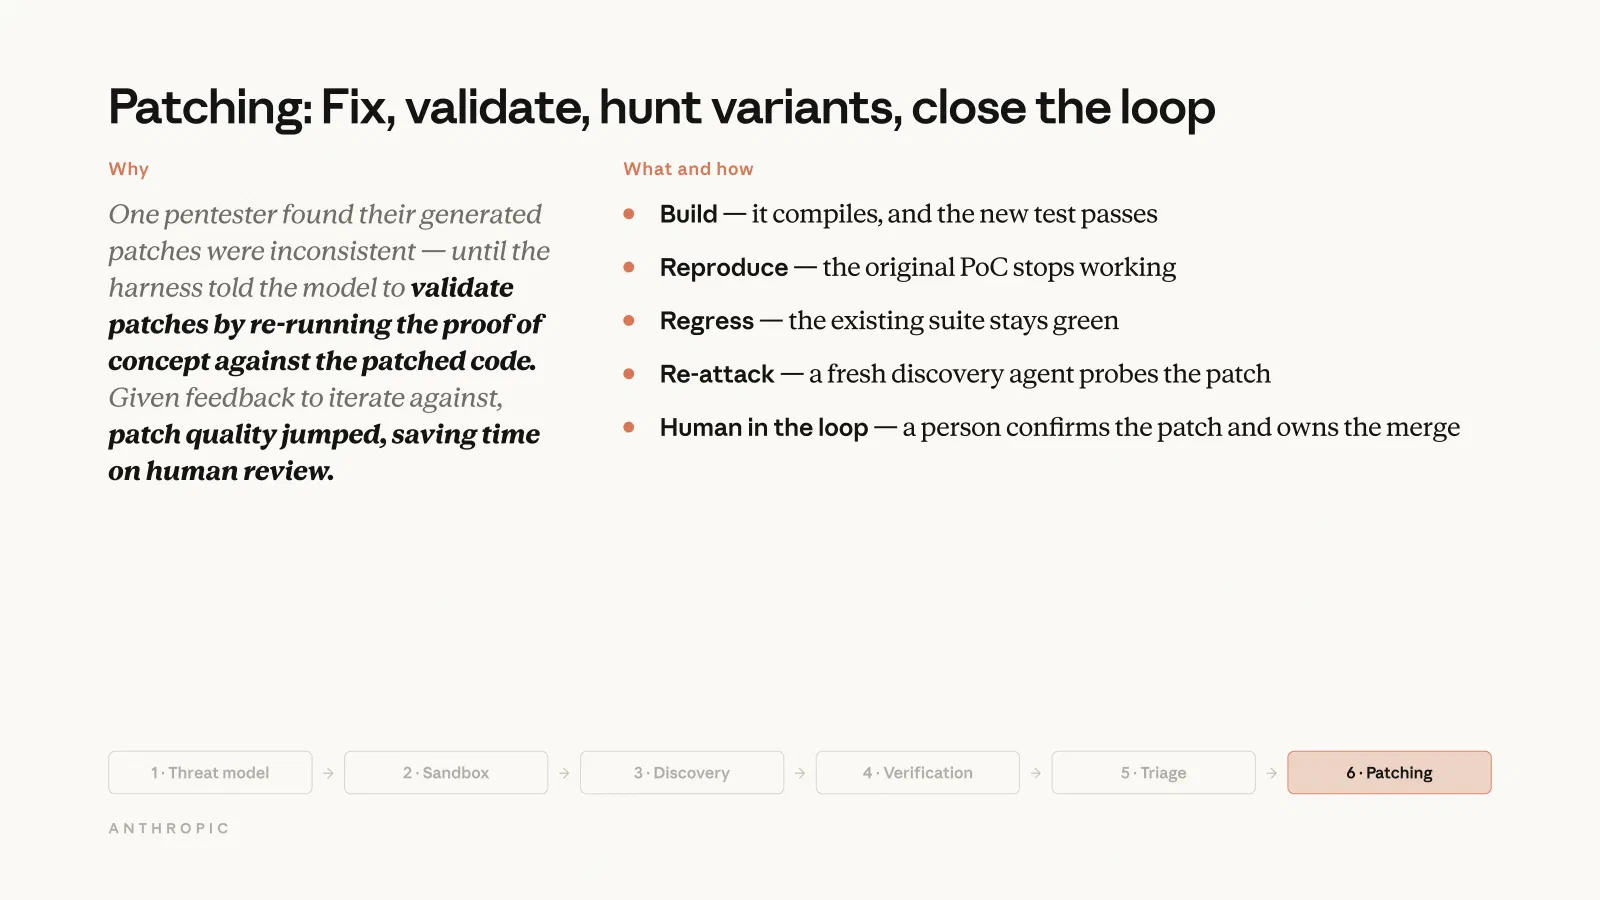
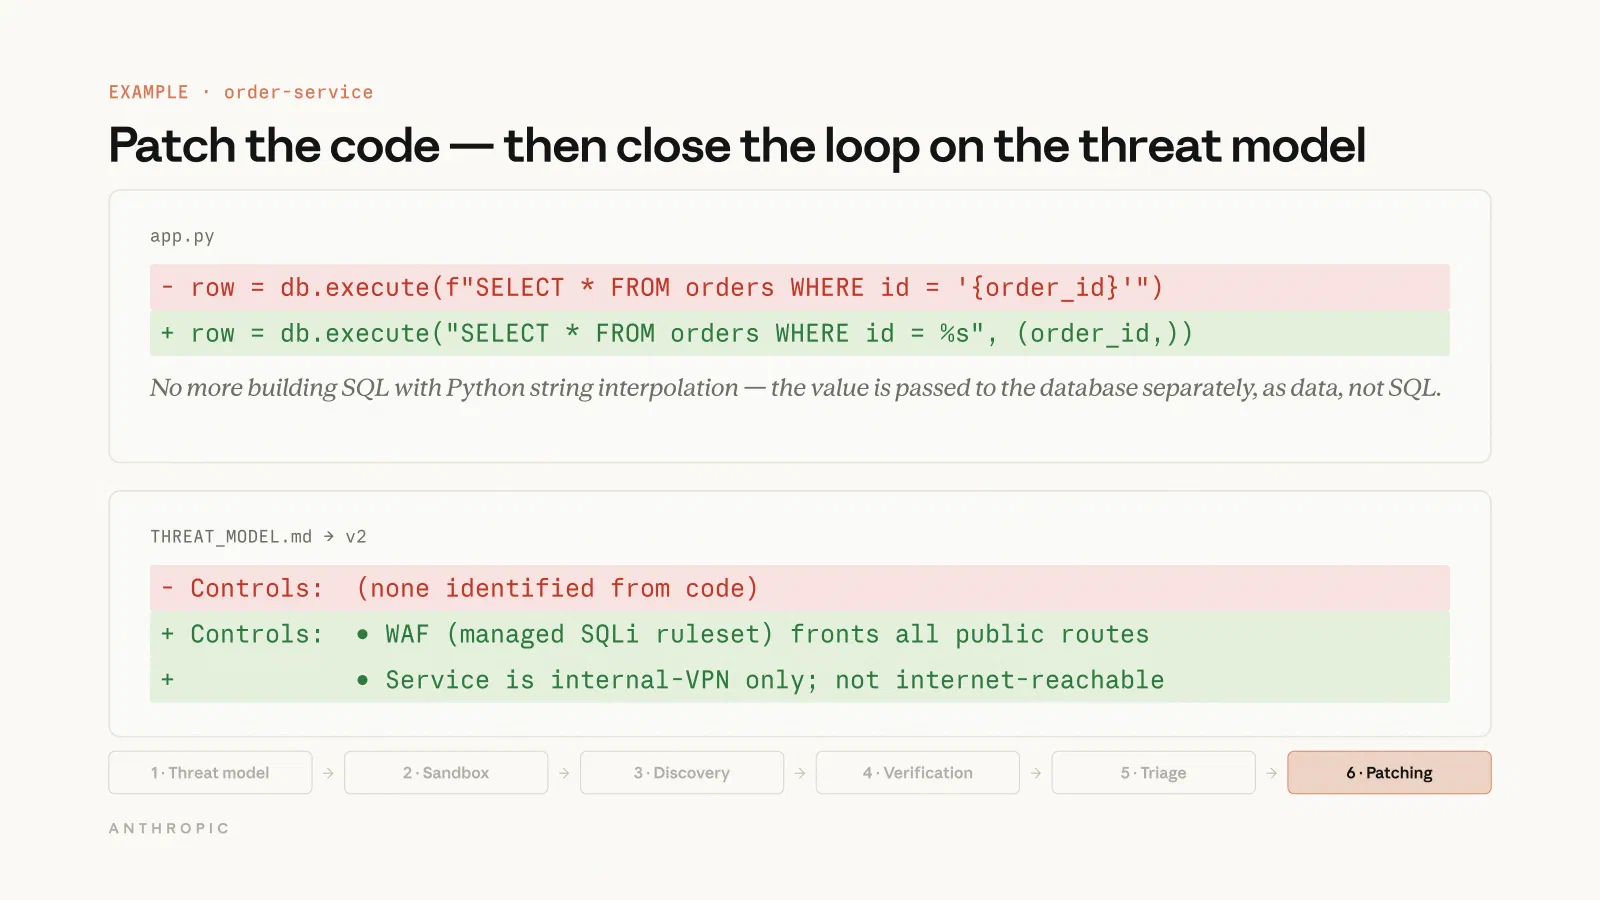
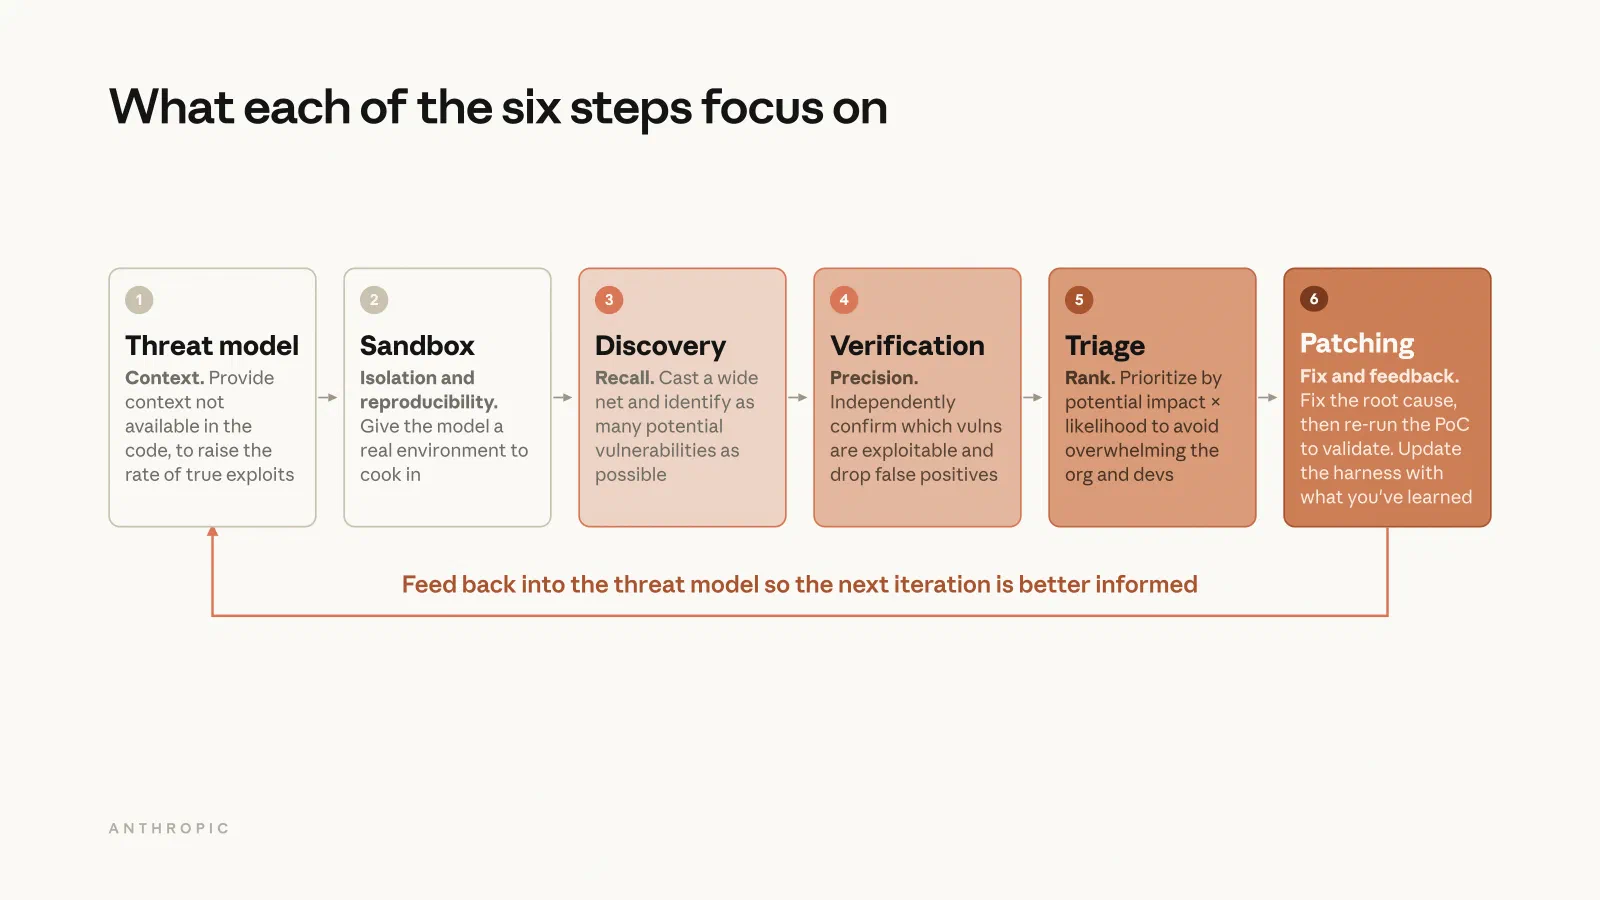
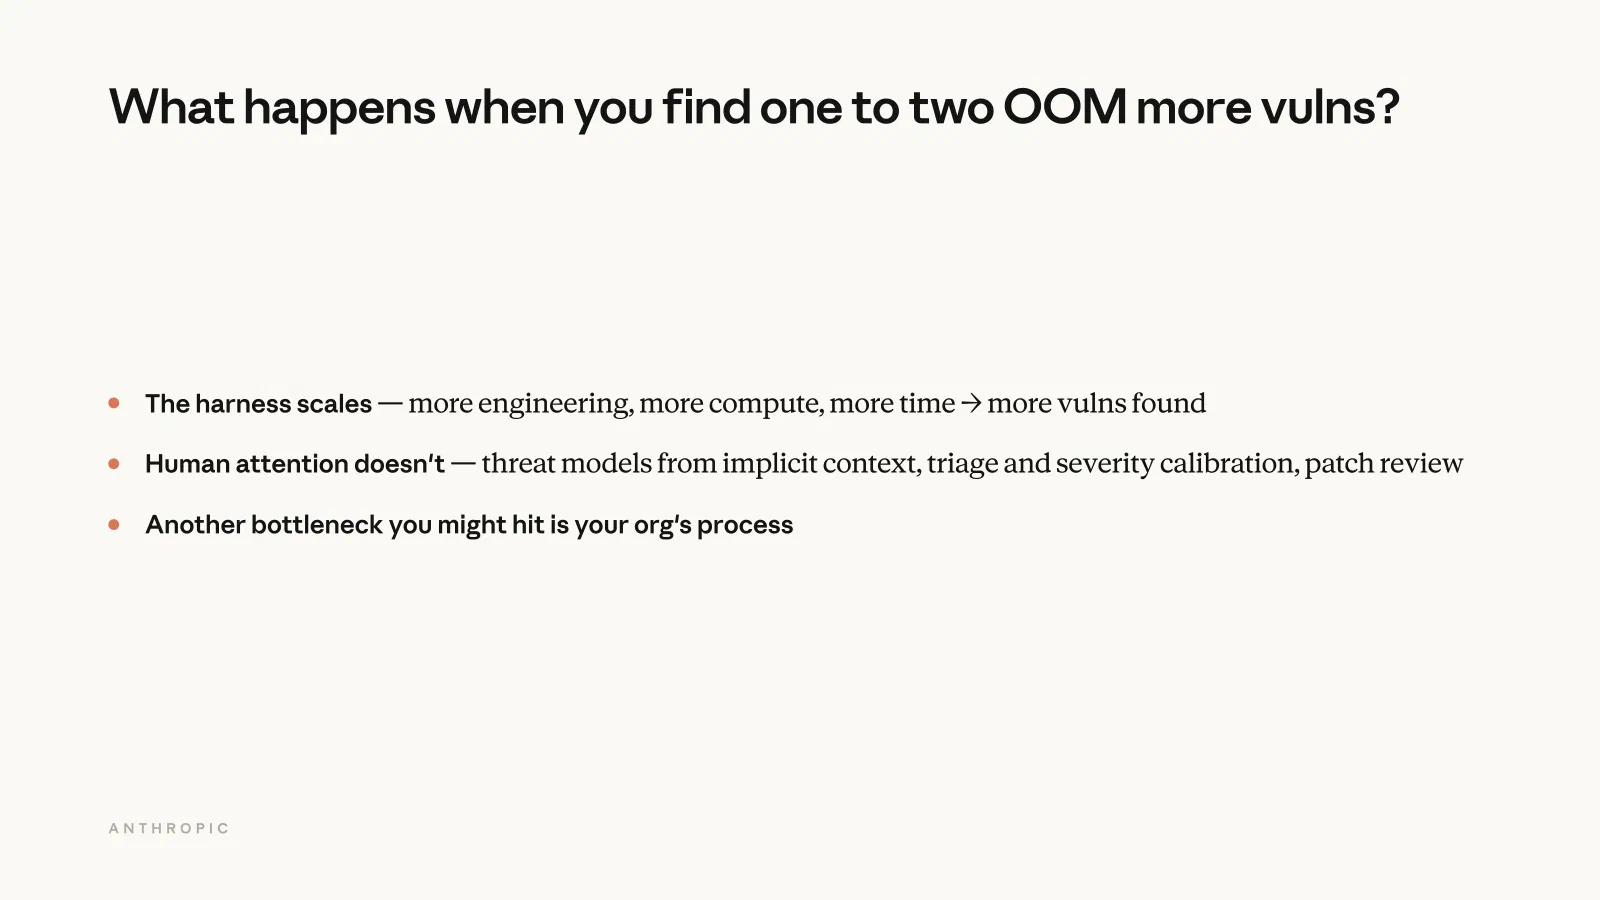
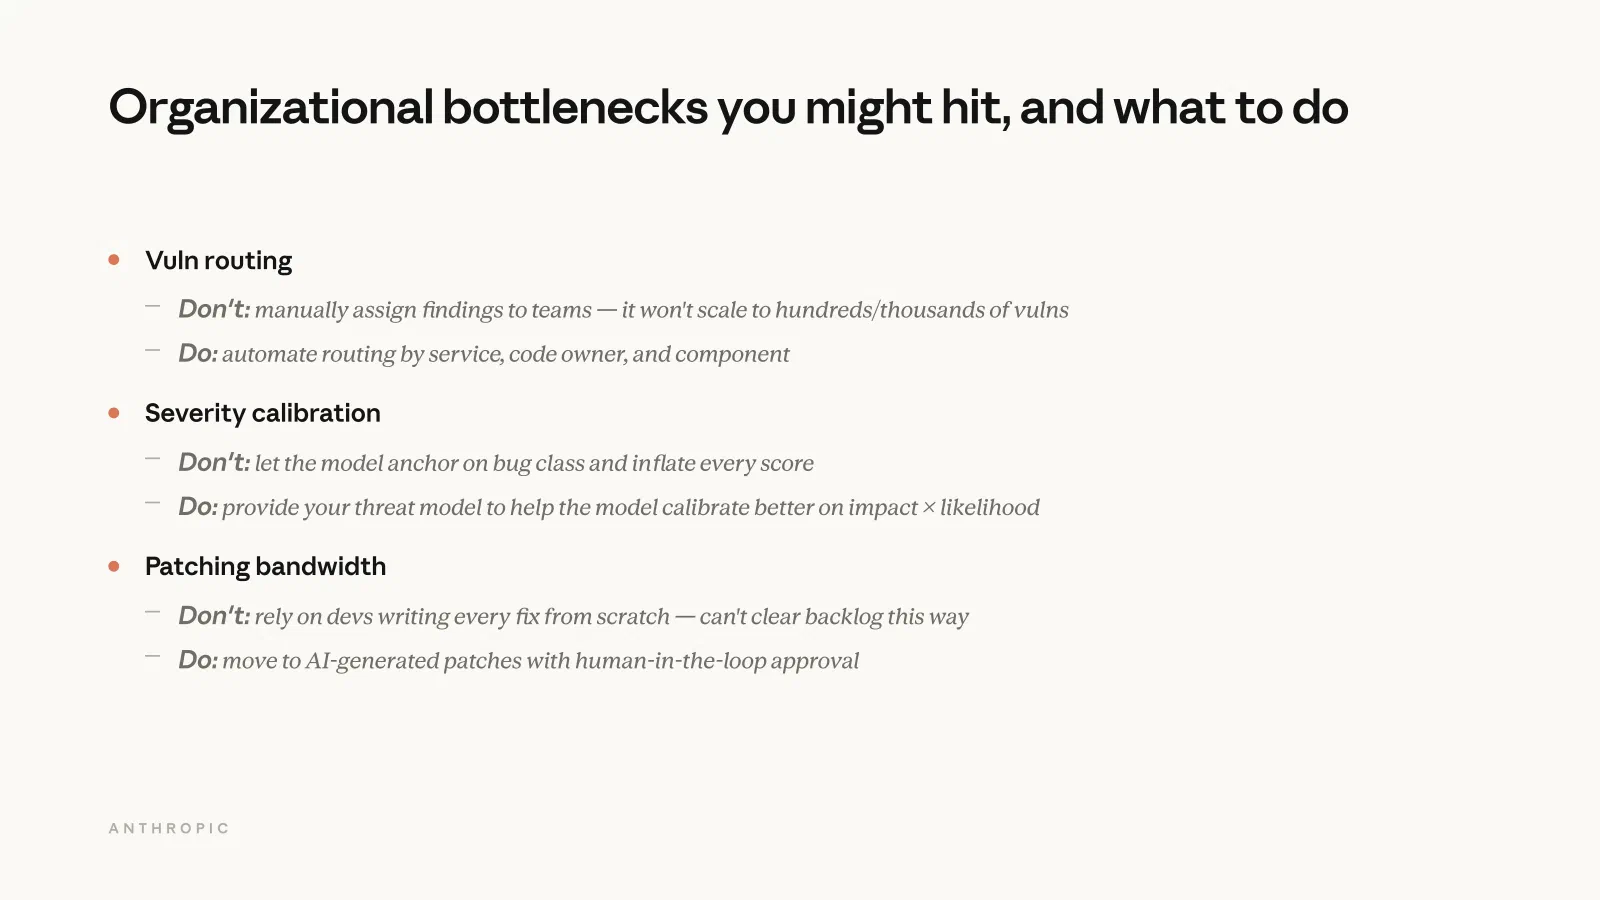
I spoke at the AI Engineer World’s Fair 2026 in San Francisco on using LLMs to secure source code: why now, six steps to building your own agentic harness for security, and the org bottlenecks that show up once finding vulnerabilities gets easy.
Here are the slides. The AI Engineer talk page has the recording, chapters, and transcript, and the write-up has the field lessons behind the talk.
Resources #
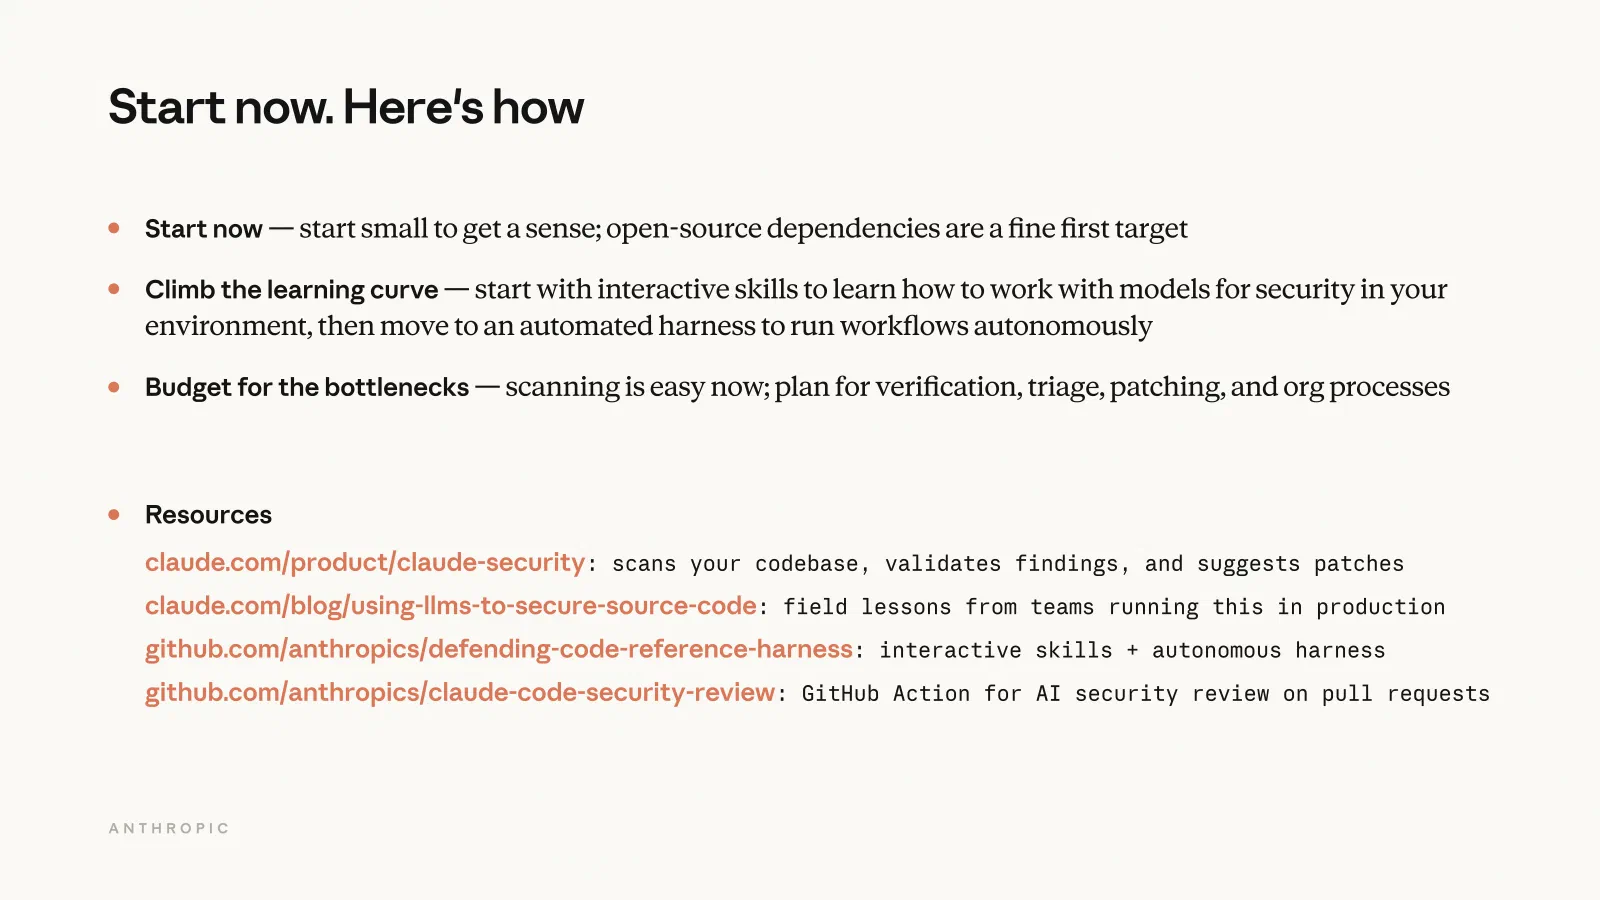
- Claude Security: scans your codebase, validates findings, and suggests patches
- Using LLMs to secure source code: field lessons from teams running this in production
- defending-code-reference-harness: interactive skills and an autonomous harness
- claude-code-security-review: a GitHub Action for AI security review on pull requests